Technical
Understanding DDoS Attacks: Real-Life Examples and How to Stop Them
Some attacks steal data. Some attacks spy on users. And some attacks have only one goal: to make your service unavailable. DDoS attacks fall into the latter category, and they are more common and more accessible to attackers than many organizations realize. They don't require exploiting a specific vulnerability or gaining access to internal systems.…
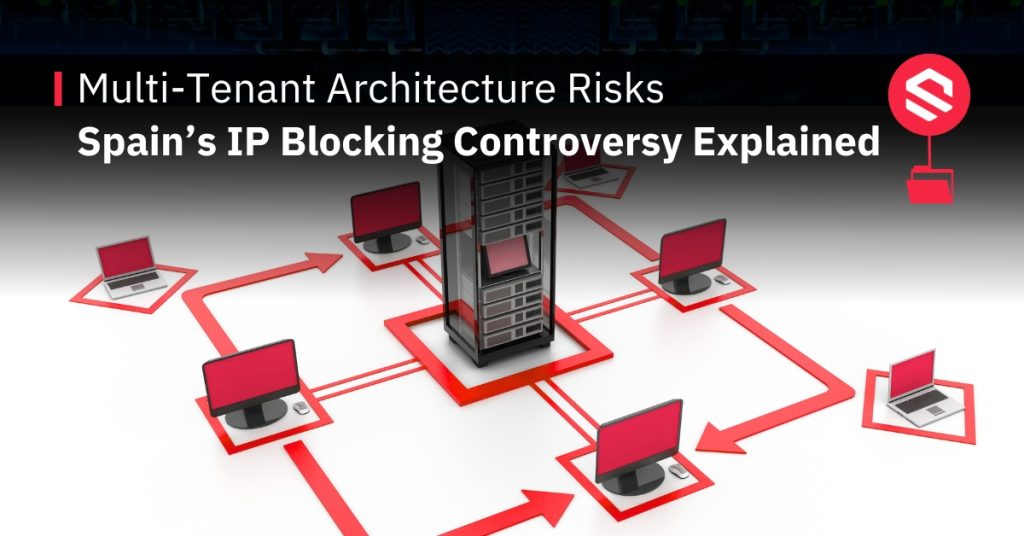
Multi-Tenant Architecture Risks: Spain’s IP Blocking Controversy Explained
In early 2025, internet users across Spain began experiencing something unexpected: legitimate websites going dark, developer tools becoming unreachable, and businesses losing access to their own online services. GitHub, GitLab, Docker registries, corporate websites, and e-commerce platforms all affected not by a cyberattack, not by a provider outage, but by a court-ordered IP block targeting…
What Happens When Modern Applications Fail Under Pressure
Together with Bluella, we've hosted a live technical webinar around a problem that many infrastructure and cybersecurity teams eventually face: What actually happens when applications start failing under pressure? Not in theory. Not in a slide deck. But in real environments, with real traffic, real attacks, and real operational stress. From the beginning, the idea…
OWASP CRS and Fail Fast: Improving Attack Detection in WAFs and Reverse Proxies
In web application security, detecting attacks as early as possible is critical. Every millisecond that a malicious request travels through an infrastructure increases backend exposure and consumes unnecessary resources. Web Application Firewalls (WAFs) based on the OWASP Core Rule Set (CRS) have become one of the most widely used mechanisms to protect applications against attacks…
When Open Source Infrastructure Stops Being Easy to Operate
Open Source infrastructure is often a deliberate and well-reasoned choice. It offers transparency, control and a level of flexibility that fits well with how many engineering teams like to build and operate systems. Deploying an open source load balancer or reverse proxy is usually a conscious decision, backed by solid documentation, community knowledge and proven…
Why multi-tenant proxies make security decisions harder for applications
In recent weeks, several incidents surfaced where content providers blocked traffic coming from multi-tenant proxies to stop automated attacks or illegal rebroadcasting. The countermeasure reduced the offensive surface, but also denied access to legitimate users travelling through the same channel. It illustrates a common issue: upstream security — security applied at proxies, CDNs or scrubbing…
High availability is not redundancy — it’s operational decision-making
For years, high availability (HA) was treated as a redundancy problem: duplicate servers, replicate databases, maintain a secondary site and ensure that if something failed, there was a plan B waiting. That model worked when applications were monolithic, topologies were simple, and traffic variability was low. Today the environment looks different: applications are split into…
Cloud security works, but not as a unified system
Talking about cloud today is no longer about a technological trend, but about a central piece of the business. More and more companies are moving their infrastructure to cloud providers under the promise of less hardware, less maintenance, fewer licenses and less time spent on activities that do not generate value. Much of that promise…
How to Evaluate a WAF in 2026 for SaaS Environments
Web applications and APIs are now the operational core of most digital services. They process transactions, expose business logic, manage identities, and connect distributed systems that evolve continuously. In parallel, the volume and sophistication of attacks has increased, driven by automation, accessible tooling, and cloud-specific attack vectors. Web Application Firewalls remain a critical part of…
